 NexAIX-官方博客
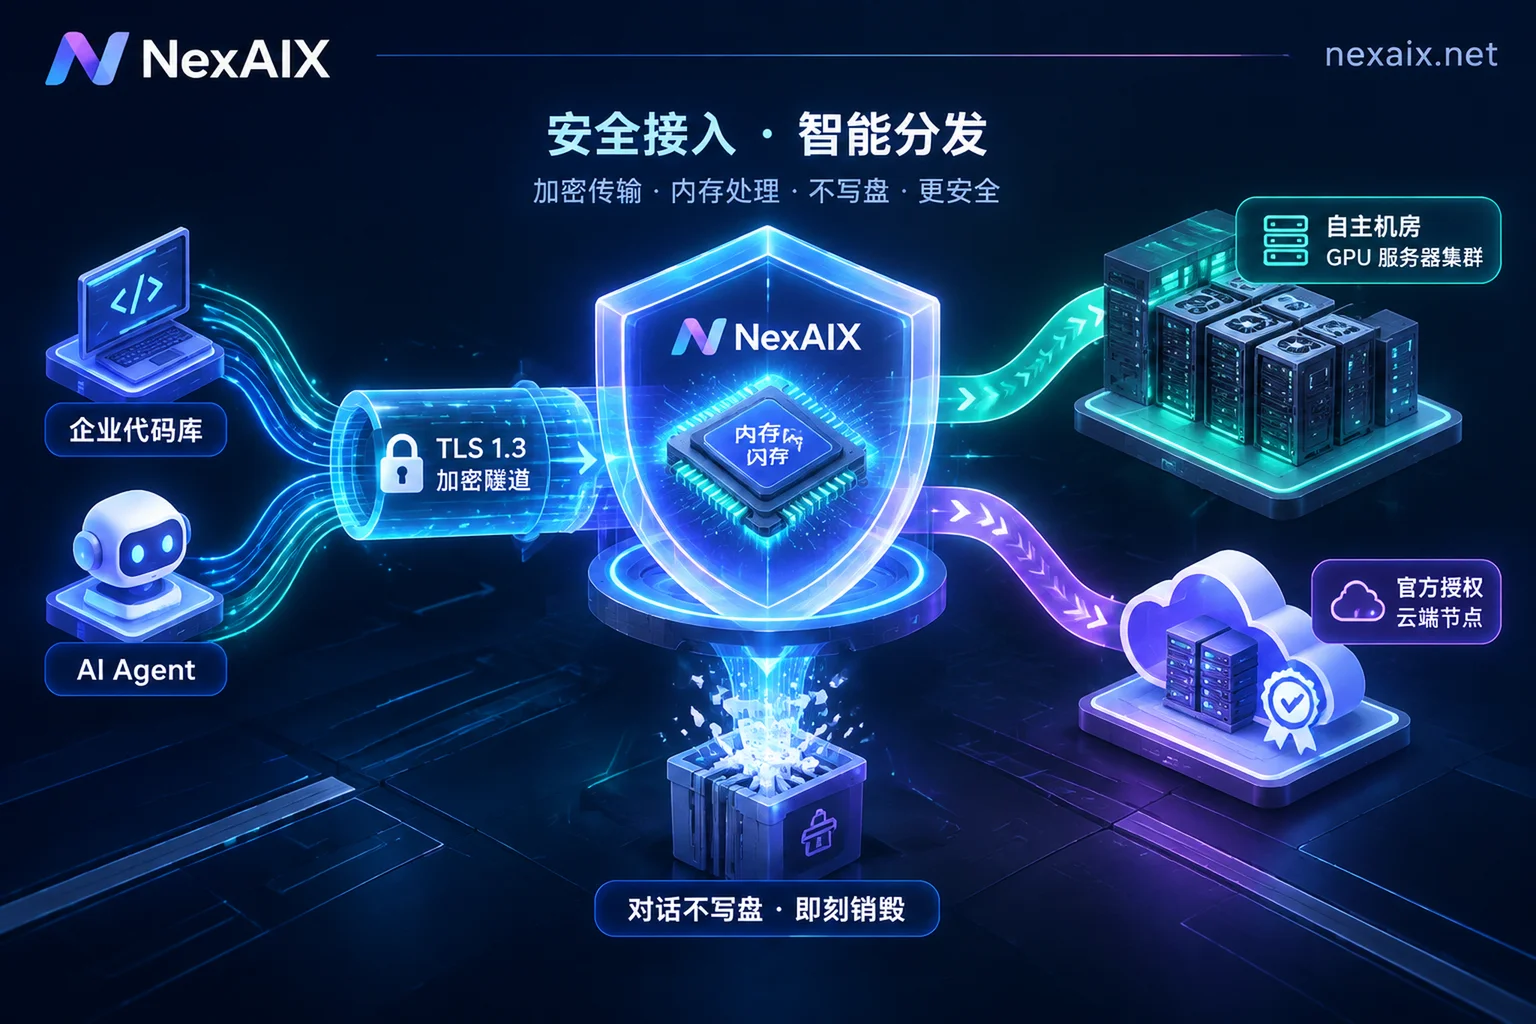
AI API Privacy Compliance in Practice: Addressing Agent Data Leaks, Upstream Retention Divergence, and Building Production-Grade Defenses
As AI Agents delve into enterprise codebases and security log analysis, AI API privacy has evolved from mere contractual terms to a core defense line in production architecture. This article combines recent security热点 to dissect data exposure points in API call chains and provides a complete practical solution from in-memory zero-logging at the gateway, separation of closed-source and open-source models, to multi-key permission isolation.
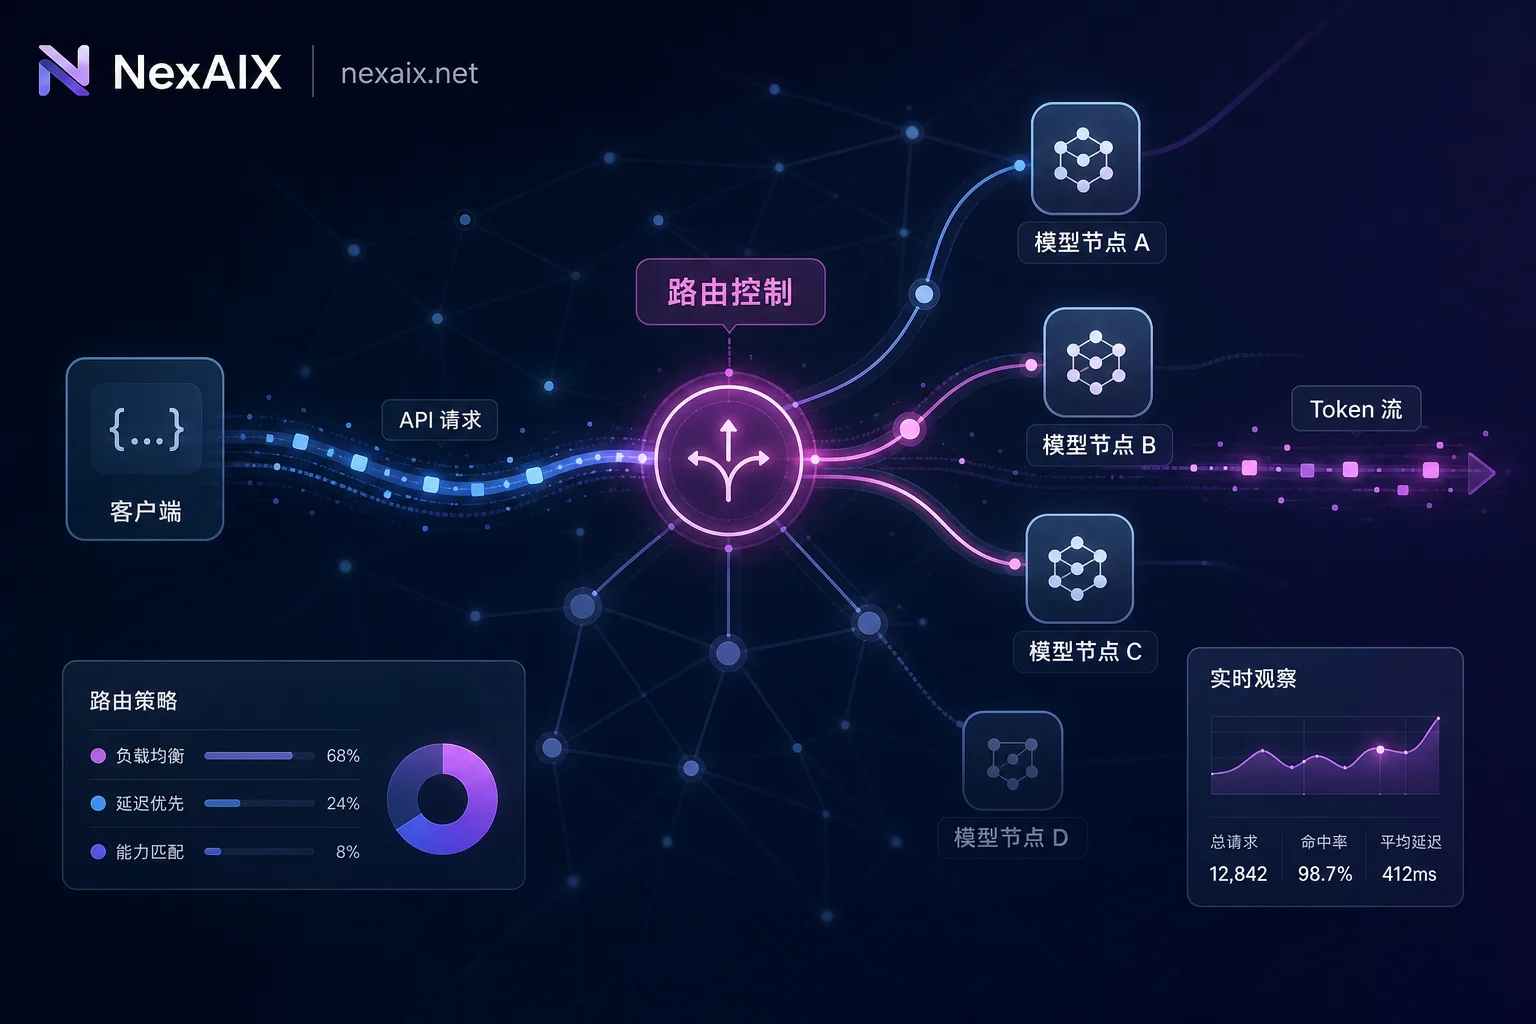
Locking Models and Disabling Automatic Routing on AI API Aggregators: Request Configuration and Verification
A practical guide to explicitly locking models, binding upstream providers, and disabling fallback on AI API aggregators, with a triple cross-check method to ensure output consistency and avoid silent degradation.